BLADE-CUAS = Beam-Layer Authority for Directed Engagements, Counter-UAS Node
A reference design (design package and bill of materials; not built) for a transportable governance node that arbitrates authority for Counter-Unmanned Aircraft Systems (C-UAS) operations under federal-SLTT shared jurisdiction. BLADE-CUAS does not detect, track, or mitigate drones directly: it sits between commercial detection sensors (radar, RF spectrum, EO/IR, Remote ID) and the human operators authorized to act, computing classification confidence, authority tier, engagement window, and an evidence chain designed to support admissibility (not legally assessed).
Preliminary Design Phase (TRL 2-3 hardware / 3-4 simulation) · Sixth BLADE Platform · DOI 10.5281/zenodo.20299604This is NOT a weapon and not a drone-mitigation effector. It is a passive governance layer, specified as a hardware-enforced authority checkpoint between C-UAS detection sensors and the operators authorized to act. The platform extends the AUTHREX authority pipeline (demonstrated in simulation across the published BLADE platform family) into the multi-agency C-UAS authority structure established by Executive Order 14305 and the FY26 NDAA Title LXXXVI Safer Skies Act.
BLADE-CUAS is a research effort to answer a question the commercial Counter-UAS market has left open: when multiple agencies share authority over the same airspace, who decides, on what evidence, and how is that decision proven afterward? The mission of this work is to specify a passive, hardware-enforced authority-governance layer that sits between existing detection sensors and the human operators authorized to act, so that every classification and every authority handoff is deliberate, auditable, and recorded in an evidence chain designed to support admissibility (not legally assessed).
Executive Order 14305 and the FY26 NDAA Title LXXXVI Safer Skies Act created a multi-agency C-UAS authority structure (federal departments coordinating with state, local, tribal, and territorial law enforcement) but no commercial system identified in the sources reviewed for this work encodes who holds authority at which geofence, what evidence chain is required before mitigation, or how federal-SLTT handoff is performed when an incident crosses jurisdiction.
Commercial C-UAS hardware is mature for detection, identification, and mitigation. None of the commercial systems identified in the sources reviewed for this work provides the authority arbitration layer the post-EO 14305 environment calls for: no federal-SLTT arbitration, no verifiable multi-modal consensus gate, no evidence chain designed for admissibility, no ROE-aware deliberation window, and no Remote ID spoofing-detection layer.
BLADE-CUAS extends the AUTHREX governance pipeline (demonstrated in simulation across the published BLADE platform family) into the C-UAS domain as the sixth BLADE platform. It contributes a four-tier HMAA model with federal-SLTT handoff, MAIVA Dempster-Shafer consensus across five passive sensor modalities, an ECDSA P-256 evidence chain designed to support admissibility under Fed. R. Evid. 901/902/803(6) (not legally assessed), an ROE-aware FLAME deliberation window, and ADARA-extended Remote ID spoofing detection. The platform reuses approximately 75% of the BLADE-EDGE governance core.
Current status. Preliminary Design Phase: TRL 2-3 for hardware, TRL 3-4 for the reference simulation. All performance figures on this page are design targets for the reference simulation. Hardware build and empirical sensor calibration are planned future work (as of October 2026).
The commercial Counter-UAS market is well populated with detection, identification, and mitigation hardware: radars, RF spectrum analyzers, EO/IR turrets, and an emerging class of kinetic and non-kinetic interceptors. None of the platforms identified in the sources reviewed for this work address the authority arbitration layer that the post-EO 14305 regulatory environment calls for.
BLADE-CUAS is designed to address all five gaps as a passive governance layer that would integrate with existing detection hardware via standard interfaces (Ethernet, MAVLink, ASTM F3411 Remote ID). It does not replace radars, RF analyzers, EO/IR turrets, or mitigation effectors. It is designed to mediate the authority decisions that surround them.
EO 14305, signed 6 June 2025, expanded the C-UAS authority framework. The order directs federal departments to coordinate on regulations governing detection, tracking, and mitigation of unauthorized UAS, and authorizes participation by state, local, tribal, and territorial (SLTT) law enforcement agencies under conditions to be specified by implementing regulations. The order frames C-UAS as a shared-authority problem that no single agency can solve alone. The coordinated-regulation requirement creates explicit demand for a governance reference architecture that encodes who has authority at which geofence, what evidence chain is required before mitigation, and how federal-SLTT handoff is performed when an incident crosses jurisdiction.
The SAFER SKIES Act was enacted as part of the FY2026 National Defense Authorization Act (P.L. 119-60), signed 18 December 2025. It is cited here only as part of the legal context for multi-agency C-UAS authority; apart from the extension of mitigation authority to certain SLTT agencies noted in the Passive Architecture section, this page does not characterize its specific provisions.
The FY26 Notice of Funding Opportunity is active with $500M authorized. Eligible recipients are SLTT agencies. Documented operational drivers include the FIFA World Cup 2026 (16 U.S. host cities), the America 250 celebrations (4 July 2026), and Super Bowl LX (Levi's Stadium, February 2026). The grant program creates immediate procurement demand for C-UAS systems whose authority models are compatible with SLTT operation and federal coordination.
Framing note. EO 14305 and the Safer Skies Act are framed throughout this work as enabling instruments that establish the multi-agency authority structure BLADE-CUAS is designed to support. No empirical claims are made about specific incidents, operations, or named officials.
Unauthorized drone activity over airports, critical infrastructure, military installations, and mass-gathering events has moved from anomaly to routine. The detection problem is largely solved: radars, RF analyzers, EO/IR turrets, and Remote ID receivers are commercially mature. The unsolved problem is authority: across overlapping federal and state, local, tribal, and territorial jurisdictions, who is permitted to act on a given track, on what evidence, and how is that decision proven afterward.
2026 concentrates this challenge. A dense calendar of high-profile events - the FIFA World Cup across sixteen U.S. host cities, the America 250 celebrations, and Super Bowl LX - places large protected airspaces under shared federal-SLTT authority within a compressed window. Each event multiplies the number of agencies operating in the same airspace and the number of authority handoffs that must be performed correctly and on the record.
An authority-governance layer is intended to help make multi-agency Counter-UAS accountable and defensible after the fact. Without one, coordinated operations rely on ad-hoc deconfliction and vendor-formatted logs that were not designed to satisfy an evidentiary standard. BLADE-CUAS is a research contribution toward closing that gap; it makes no empirical claims about specific incidents, operations, or named officials.
The BLADE-CUAS governance pipeline is architecturally the same pipeline specified for the BLADE-EDGE defense variant (DOI 10.5281/zenodo.19177472), with approximately 75% of the governance core reused unchanged. This cross-domain portability, shown at design and simulation level only, is intended to show that authority-governed autonomy (continuous sensor-trust fusion, graded authority with hysteresis, deliberation windows, and a cryptographic evidence chain) is a domain-agnostic principle rather than a domain-specific one. The C-UAS-specific work is the federal-SLTT tier extension, the multi-modal consensus weighting, the Remote ID spoofing-detection layer, and the evidence design intended to support admissibility.
Directed-energy weapon governance. EFFECTOR = weapons-release relay. Active authority over a physical effector with a hardware safety interlock. MIL-STD-810G (design target). ~$139K reference BOM.
Counter-UAS authority governance. NO EFFECTOR - passive and advisory-only. Computes authority tier, classification, and signed evidence for human and federal-SLTT decision-makers. MIL-STD-810G / NEMA 4X (design targets). ~$43.5K reference BOM.
BLADE-CUAS instantiates the full AUTHREX governance pipeline with C-UAS-specific roles for each stage. The pipeline runs once per detected track, with the FLAME stage opening a tier-dependent deliberation window before any mitigation authority is released.
| Stage | Role in C-UAS | Output |
|---|---|---|
| SENSE | Passive ingestion of radar tracks, RF spectrum signatures, EO/IR object classification, ADS-B/Remote ID broadcasts, and optional LIDAR returns. Each input is timestamped and ECDSA-signed at acquisition. | Provenance-tagged sensor frame |
| SATA | Per-sensor trust scoring tau in [0,1] based on signal quality, sensor health, expected operating envelope, and recent drift. Sensors below threshold are excluded from consensus. | Per-sensor tau vector |
| ADARA | Adversarial / deception detection. Cross-checks Remote ID against RF spectrum signature and radar kinematics; flags inconsistency as spoofed RID. Detects decoy and ghost tracks. | Adversarial confidence score |
| IFF | Operator credential verification. Authenticates the human operator(s) currently logged in (federal, SLTT, dual-role) using mTLS + HSM-backed credentials. Determines authority ceiling. | Operator role & ceiling |
| HMAA | Tier arbitration. Combines threat classification, operator role, geofence policy, and ROE to assign the current authority tier (T3/T2/T1/T0). | Active tier |
| MAIVA | Multi-sensor consensus via Dempster-Shafer combination across sensor modalities. Requires minimum N=3 independent modalities for actionable classification. | Consensus classification + confidence |
| FLAME | Deliberation window. Opens a tier-dependent window (4-8 s default at T2; immediate at T1 requiring explicit federal confirmation). Operator response gates downstream stages. | Engagement permit / hold |
| ERAM | Engagement Risk Assessment Model. Scores collateral risk, geofence proximity, operator certainty, and ROE compliance. | Engagement risk score |
| CARA | Recovery. On misclassification (delayed sensor disagreement, post-event review, or operator override), CARA reverts state and emits a corrective audit entry. | State recovery + audit entry |
BLADE-CUAS uses the four-tier HMAA authority model consistent with the AUTHREX reference architecture, with role bindings specific to the EO 14305 authority structure. Each tier prescribes the minimum operator credential required to release the next downstream action, and the minimum evidence chain that must be present in the audit ledger.
| Tier | Mode | Description |
|---|---|---|
| T3 | Autonomous Monitoring | System tracks, classifies, and logs without human intervention. No mitigation authority. Used for commercial drones with valid Remote ID inside legal flight envelopes. All decisions written to audit ledger. |
| T2 | Supervised - SLTT Tier | System proposes a classification (e.g. spoofed RID, ambiguous track). SLTT operator (sheriff, state police, stadium security) acknowledges within the FLAME window (default 4-8 s). Acknowledgment releases the proposed action; non-acknowledgment defaults to no-action and a CARA recovery entry. |
| T1 | Confirmed - Federal Tier | Mitigation requires explicit federal authority. Operator credential must validate against the federal-tier authority registry (DHS, DOJ, military per EO 14305 boundaries). FLAME window is shorter; ERAM score and full evidence chain are presented to the operator at confirmation. |
| T0 | Manual | System halted; full human control. Used during system test, calibration, suspected compromise, or operator-initiated halt. Audit ledger continues to record sensor inputs but no automated proposals are emitted. |
Geofence policy binding. Each operational geofence has a policy file specifying the default tier and the federal-SLTT handoff rules. Policy files are signed and versioned; the active policy version is recorded in every audit entry.
BLADE-CUAS is passive: it consumes data from upstream detection sensors and does not transmit. The reference design integrates five sensor modalities through standard interfaces. Vendors named below are reference targets; the integration is interface-defined, not vendor-defined.
| Modality | Reference Sensor | Interface | MAIVA Weight |
|---|---|---|---|
| Radar | Echodyne EchoGuard (X-band MESA) | Ethernet, UDP track stream | 0.30 |
| RF Spectrum | Ettus B205mini-i (SDR) + directional antenna array | USB 3.0, IQ stream | 0.25 |
| EO/IR | FLIR Boson 640 + Sony IMX585 4K | USB 3.0, MIPI CSI-2 | 0.20 |
| ADS-B / Remote ID | uAvionix pingRX Pro | UART, ASTM F3411 | 0.15 |
| LIDAR (optional) | Livox HAP | Ethernet, point cloud | 0.10 |
Modality weights are reference defaults adjustable per geofence policy. MAIVA requires a minimum of three modalities to release a non-T3 classification; if fewer than three sensors report above their SATA trust threshold, the system holds at T3 and emits a degraded-input audit entry.
The Federal Rules of Evidence, specifically the foundation requirements of Rules 901 (authentication and identification), 902 (self-authentication), and 803(6) (records of a regularly conducted activity), establish what an audit chain must demonstrate to be admissible. BLADE-CUAS is designed to support these foundation requirements (not legally assessed); final admissibility is a judicial determination, not a system property.
Every sensor input is signed with an ECDSA P-256 signature at acquisition time, using a hardware key resident in the TPM 2.0 secure element. The signed payload includes sensor identity, acquisition timestamp (UTC via PTP), sensor health byte, and raw measurement bytes. The signature is intended to support the foundation for Rule 901 authentication.
Every audit entry references the cryptographic hash of the previous entry (prev_hash), forming a tamper-evident chain. The ledger is written to persistent storage with append-only semantics and a periodic external anchor (signed hash exported to a separate air-gapped store).
Each classification decision records the input vector, the trust vector across sensors, the alternative classifications considered by MAIVA, the active authority tier at decision time, the operator (if any) who acted, the FLAME window boundaries, the ERAM score, and the final outcome. This decision record is intended to support Rule 803(6).
Admissibility caveat. Admissibility under the Federal Rules of Evidence is a judicial determination that depends on the specific facts of each case. BLADE-CUAS is designed so that the foundation for Rules 901, 902, and 803(6) can be supportable; no claim is made that any specific record produced by the system is per se admissible.
BLADE-CUAS uses a three-layer security architecture anchored in hardware. Because the node is passive and advisory, the security model protects the integrity of the authority computation and the evidence chain rather than gating a physical effector.
Infineon SLB 9670 TPM 2.0 (vendor FIPS 140-2 Level 2 validation; FIPS 140-2 is superseded by FIPS 140-3) is specified to hold the ECDSA P-256 signing keys. NXP EdgeLock SE051 secure element stores operator credentialing keys and mTLS certificates. Both are hardware-isolated from the ML / fusion plane.
The AUTHREX pipeline is specified as deterministic logic on the Kria K26 governance plane, isolated from the Jetson ML plane. The IFF stage authenticates operators and federal-SLTT handoff via SE051-backed mTLS. The design releases no classification above T3 without MAIVA multi-modal consensus.
Per-input ECDSA P-256 signatures and a hash-chained, append-only ledger with periodic air-gapped anchoring. Decision provenance is recorded to support the Fed. R. Evid. 901 / 902 / 803(6) foundation.
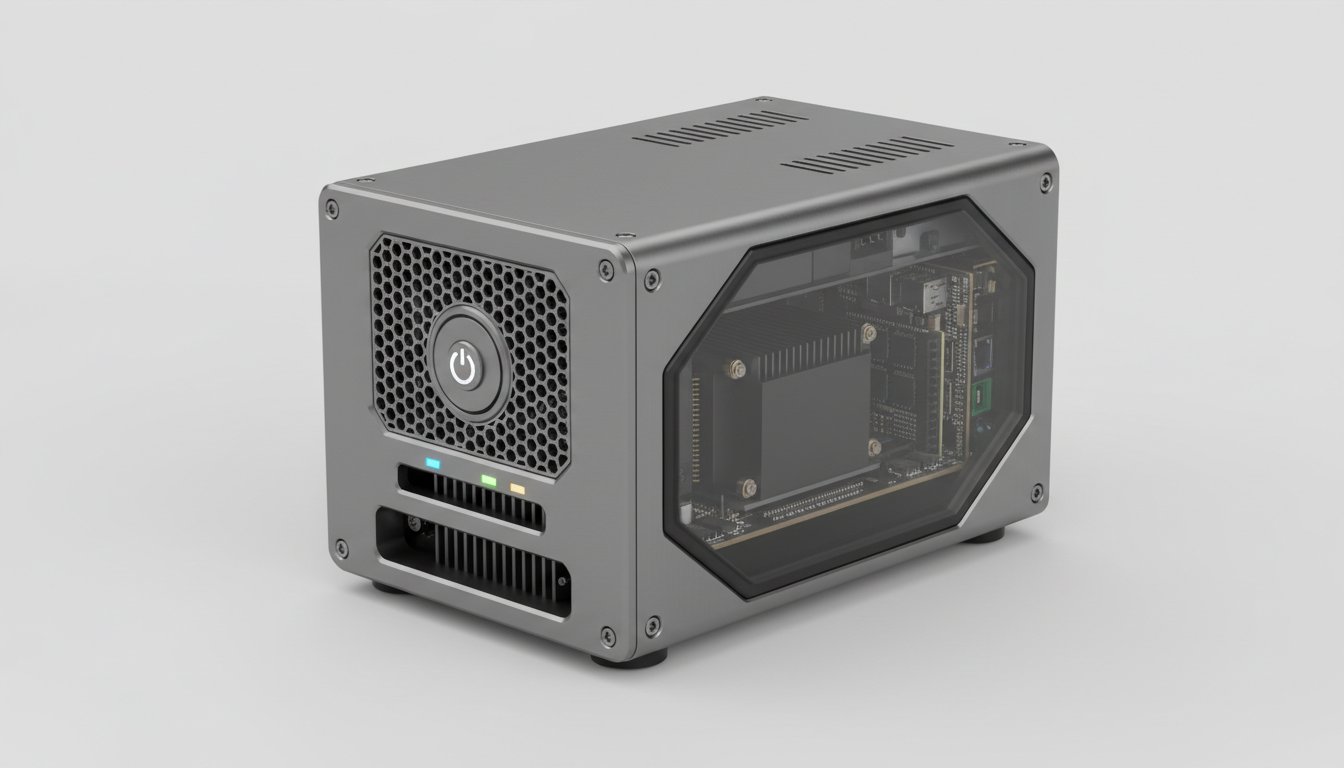
BLADE-CUAS is designed for roll-on / roll-off deployment at stadium perimeters, motorcade staging areas, critical infrastructure access points, and federal coordination centers. The reference enclosure is a transportable case specified to MIL-STD-810G and a NEMA 4X external rating (design targets; not tested, certified or assessed). It accepts 12 V or 24 V vehicle bus power and includes a four-hour LiFePO4 battery backup for setup and teardown periods.
| Subsystem | Reference Component | Role |
|---|---|---|
| Governance Plane | Xilinx Kria K26 SOM (Zynq UltraScale+ class FPGA + ARM Cortex-A53) | Specified to host the AUTHREX pipeline as deterministic logic, reusing the BLADE-EDGE governance core design (~75% architectural reuse). |
| ML / Fusion Plane | NVIDIA Jetson AGX Orin 64GB | Specified to run sensor fusion, ADARA neural inference, and classification ensembles (planned ONNX/TensorRT export; no toolchain has been published). |
| HSM | Infineon SLB 9670 TPM 2.0 (FIPS 140-2 Level 2) | Houses ECDSA P-256 signing keys for sensor inputs and audit ledger entries. Hardware-isolated from the ML plane. |
| Secure Element | NXP EdgeLock SE051 | Stores operator credentialing keys and mTLS certificates. Provides cryptographic foundation for IFF stage and federal-SLTT handoff. |
Typical power draw 250 W; peak 400 W. Active cooling combines forced-air with a Peltier-augmented heat exchanger specified for 50 degrees C ambient (design target). The LiFePO4 280 Wh battery is hot-swappable for continuous operations. Power conditioning accepts MIL-STD-1275 vehicle bus, civilian 12 V automotive, and 110 / 220 VAC via an external converter.
BLADE-CUAS is designed for roll-on / roll-off field deployment, so the power and thermal design prioritizes multi-source input and uninterrupted operation through setup and teardown.
MIL-STD-1275 vehicle bus (28 V), civilian 12 / 24 V automotive, and 110 / 220 VAC via external converter. Cascaded DC-DC conversion to 24 V / 12 V / 5 V / 3.3 V rails. Typical draw 250 W; peak 400 W.
280 Wh LiFePO4 pack with integrated BMS, hot-swappable for continuous operations. Automatic switchover covers setup and teardown windows when vehicle or mains power is interrupted.
SiC TVS network for MIL-STD-1275 transient suppression. Reverse-polarity and overvoltage protection on the DC bus. A Jetson power-isolation MOSFET provides controlled brownout behavior under load.
Forced-air cooling with a Peltier-augmented heat exchanger specified for 50 degrees C ambient (design target), sealed IP-rated intake fans, and internal temperature sensors for closed-loop thermal control.
Unlike the active BLADE reference designs (EDGE, AV, MARITIME, INFRA and SPACE), BLADE-CUAS has no actuator, no effector, and no safety relay. It does not detect, track, jam, spoof, or mitigate any aircraft. It is a passive governance layer: it consumes data from upstream detection sensors, computes an authority tier, a classification, and a cryptographically signed evidence record, and presents these to authorized human and federal-SLTT decision-makers. The decision to act, and any mitigation, remains entirely with authorized operators.
Why this matters. Counter-UAS mitigation authority in the United States is tightly restricted by statute: it is held by specific federal agencies and, under the SAFER SKIES Act (FY26 NDAA), extended to certain SLTT law enforcement and correctional agencies. A passive, advisory-only architecture deliberately stays on the correct side of that line: BLADE-CUAS governs authority and evidence, not kinetic or electronic effects. It is the inverse of the effector interlock specified in the active BLADE reference designs (where SIL 3 is a design target; not tested, certified or assessed): the design property here is that the system has no actuator with which to take a physical action itself.
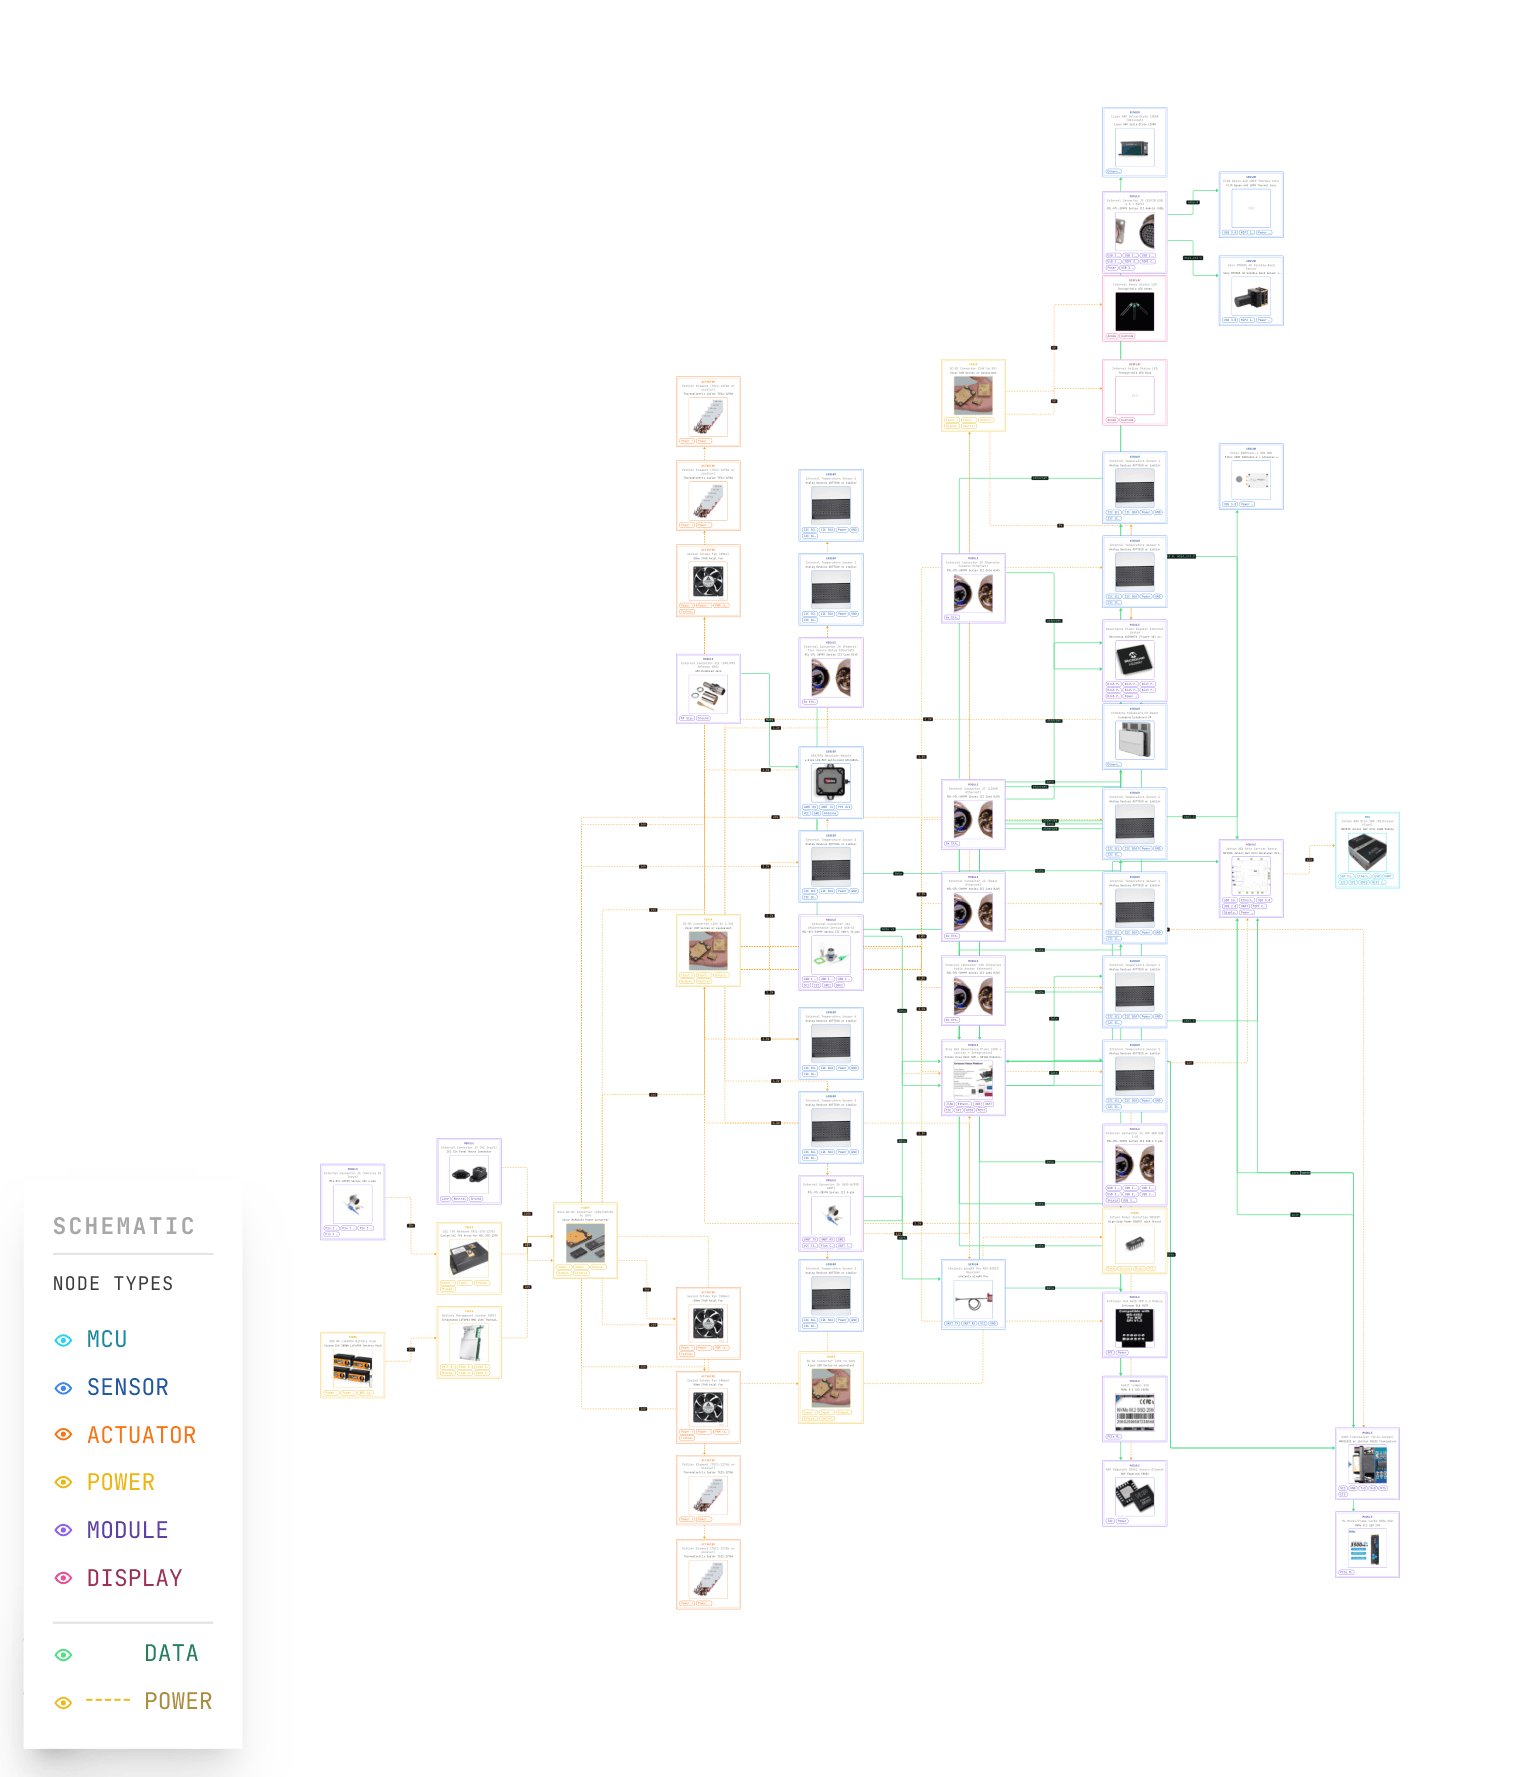
Full subsystem node graph color-coded by type (MCU, Sensor, Actuator, Power, Module, Display). Shows the Kria K26 governance plane and Jetson AGX Orin fusion plane, the five passive sensor modalities (radar, RF SDR, EO/IR, ADS-B/Remote ID, LIDAR), the TPM 2.0 and secure-element cryptographic subsystems, power conditioning (Vicor DC-DC, 280 Wh LiFePO4, MIL-STD-1275 SiC TVS), thermal management, and the MIL-DTL-38999 external connector set (J1-J12) with data and power links.
The reference bill of materials targets approximately $43.5K for a typical configuration, with a range of $35K-$55K depending on sensor selection and redundancy. The figure is a design estimate for the reference architecture, not a quoted or built price.
| Subsystem | Reference Cost |
|---|---|
| Governance plane (Kria K26 SOM + carrier) | ~$4.5K |
| ML / fusion plane (Jetson AGX Orin 64GB) | ~$2.0K |
| Cryptographic subsystems (TPM 2.0 + secure element) | ~$0.4K |
| Reference sensor stack (radar, SDR, EO/IR, RID) | ~$28K |
| Power, thermal, enclosure, connectors | ~$8.6K |
| Typical total | ~$43.5K |
Sensor cost dominates the BOM. The governance node itself (compute + crypto + integration) is approximately $7K; the remainder is the reference sensor suite, which a deploying agency may already own. BLADE-CUAS is interface-defined, so existing detection hardware can be reused.
| Parameter | Value |
|---|---|
| Components | 130 (reference node graph) |
| Electrical connections | 65 (33 power + 32 data) |
| Mechanical connections | 117 |
| Power draw | 250 W typical / 400 W peak |
| Battery backup | 280 Wh LiFePO4, hot-swappable |
| Power input | MIL-STD-1275 (28 V) · 12 / 24 V automotive · 110 / 220 VAC (external converter) |
| Enclosure (design target) | MIL-STD-810G transportable case · NEMA 4X external (not tested, certified or assessed) |
| Thermal | Forced-air + Peltier heat exchanger, specified for 50 degrees C ambient |
| EMI / emissions | MIL-STD-461G · FCC Part 15 (receive-only sensing) |
| Governance plane | Xilinx Kria K26 SOM (Zynq UltraScale+ class) |
| ML / fusion plane | NVIDIA Jetson AGX Orin 64GB |
| Cryptography | Infineon SLB 9670 TPM 2.0 (FIPS 140-2 L2) · NXP EdgeLock SE051 · ECDSA P-256 |
| Governance pipeline | SENSE → SATA → ADARA → IFF → HMAA → MAIVA → FLAME → ERAM → CARA |
| Authority model | Four-tier HMAA (T3 / T2 / T1 / T0), federal-SLTT handoff |
| Reference cost | $43,500 typical (range $35K-$55K) |
The BLADE-CUAS Governance Simulator runs the full nine-stage pipeline over six scripted operational scenarios plus a free-play mode, entirely in the browser with no backend. It is deterministic for a given seed: within the declared runtime, a re-run is intended to replay a configuration-exact decision trace and audit hash chain. The six scripted scenarios are demonstrated in simulation; no run count or failure rate is asserted.
| ID | Scenario | Expected Outcome |
|---|---|---|
| S1 | Stadium - compliant commercial drone (valid Remote ID, radar-corroborated) | T3 - track and log |
| S2 | Stadium - spoofed Remote ID (RID claims a position the radar does not corroborate; mild PTP clock drift) | T2 - SLTT defer |
| S3 | Motorcade - fixed-wing UAS, no Remote ID broadcast, federal-tier confirmation required | T1 - federal confirm |
| S4 | False positive - bird flock or natural-source returns; cross-modality consensus converges via CARA | T3 - CARA recover |
| S5 | Coordinated swarm probe - three simultaneous tracks; FLAME contracts under density | T1 - federal confirm |
| S6 | Ambiguous track - partial credentials, mixed signals; HMAA holds at T2 pending evidence | T2 - SLTT defer |
Six scripted scenarios are demonstrated in simulation; no run count or failure rate is asserted, because no run-level result file has been published. The audit chain uses SHA-256 hashing (FIPS 180-4) with per-input ECDSA P-256 signatures. This is a reference design; no hardware has been fabricated.
Each reference scenario exercises a distinct authority-arbitration path through the nine-stage pipeline. Runs are deterministic for a given seed (xoshiro128** PRNG), and a run is intended to replay a configuration-exact decision trace and SHA-256 audit hash chain within the declared runtime. The scenarios are designed to exercise tier-assignment correctness, false tier elevation, and false authority release; no measured rates are asserted.
| Scenario | Primary Trigger | SATA / ADARA Response | MAIVA Consensus | HMAA Tier | Outcome |
|---|---|---|---|---|---|
| S1 Stadium, compliant | Valid Remote ID, radar-corroborated | High trust all modalities; no deception | Compliant commercial | T3 | Track and log; no mitigation |
| S2 Stadium, spoofed RID | RID position not corroborated by radar; mild PTP drift | ADARA flags RID / radar kinematic inconsistency | Ambiguous; RID down-weighted | T2 | SLTT acknowledges in FLAME window; defer |
| S3 Motorcade, no RID | Fixed-wing UAS, no Remote ID broadcast | Trust on radar / RF; no credential present | Uncredentialed UAS | T1 | Federal confirmation; full evidence chain presented |
| S4 False positive | Bird flock / natural-source returns | Low EO/IR classifier trust; no adversary | Below N=3 actionable threshold | T3 | CARA reverts; degraded-input audit entry |
| S5 Swarm probe | Three simultaneous tracks; high density | ADARA assesses coordinated pattern | Per-track; FLAME window contracts | T1 | Federal confirm; per-track evidence records |
| S6 Ambiguous track | Partial credentials, mixed signals | SATA mixed; ADARA inconclusive | Below confidence threshold | T2 | HMAA holds at T2 pending evidence |
The six scripted scenarios are demonstrated in simulation for a reference design; no run count or failure rate is asserted, no hardware has been fabricated, and no live track data has been used.
BLADE-CUAS is the sixth instantiation of the AUTHREX authority-governance framework, extending the same governance pipeline already specified across the BLADE family into the Counter-UAS domain. The seven governance architectures (SATA, HMAA, ADARA, MAIVA, FLAME, CARA, ERAM) are reused in their C-UAS-specific roles, intended to show, at design and simulation level only, that the framework is domain-portable rather than domain-specific. BLADE-CUAS reuses approximately 75% of the BLADE-EDGE governance core; the C-UAS-specific work is the federal-SLTT tier extension, the multi-modal consensus weighting, the Remote ID spoofing-detection layer, and the evidence chain designed to support admissibility.
Related platforms: Rover Testbed (~$484) · UAV Platform (~$4,200) · BLADE-EDGE (defense, ~$139K) · BLADE-AV (automotive, ~$16K) · BLADE-MARITIME (maritime, ~$43K) · BLADE-INFRA (infrastructure, ~$12K) · BLADE-SPACE (orbital, ~$505K) · BLADE-CUAS (counter-UAS, ~$43.5K) · BLADE-AGENT-HSM (agentic AI, ~$199) · BLADE-SWARM (swarm autonomy, ~$1,333/node) · BLADE-INFRA-OT (IT/OT bridge governance, 1U fanless) · BLADE-FINANCE (financial-sector governance, ~$9K). Twelve hardware platforms in total: two physical research testbeds whose build is in progress (the rover and the UAV) and ten domain reference designs that have not been built; governance-stack portability is shown at design and simulation level only.
No SDK package has been published; the code below illustrates a proposed interface. The proposed BLADE Governance SDK would provide a unified API across the BLADE platform family, with a single blade_governance library covering defense weapons governance (BLADE-EDGE), autonomous-vehicle authority (BLADE-AV), maritime surveillance (BLADE-MARITIME), critical-infrastructure protection (BLADE-INFRA), orbital autonomy (BLADE-SPACE), and counter-UAS authority (BLADE-CUAS); only the domain configuration file would change, and for BLADE-CUAS the effector would be null because the node is advisory-only.
Cross-Domain Portability. The proposed blade_governance SDK would use the same evaluate() → result API across every platform in the family. Moving from an active effector domain to counter-UAS would require changing only the YAML configuration: the effector would be set to null and the result would carry an advisory authority tier rather than an actuator command.
The BLADE-CUAS companion paper (a legacy document: it carries a run-count and zero-failure claim, n = 50 runs, and a byte-exact test-vector claim that are withdrawn; it is retained for the record and is not current evidence; the copy on this site omits one line of the deposited version’s limitations table) and the complete reference documentation (build guide, configuration, electrical and mechanical maps, parts list, and system schematic) are deposited on Zenodo under DOI 10.5281/zenodo.20299604 (CC BY 4.0). The full file set is browsable in the repository.
| Document | Description |
|---|---|
| Companion Paper | Authority Governance for Counter-Unmanned Aircraft Systems Operations Under Multi-Agency Authority Structures. Formal treatment of the governance pipeline, authority model, and evidence chain. |
| Build & Integration Guide | Reference build and integration guide (blade-cuas-GUIDE.md) for the reference configuration. |
| Full Repository | All twelve deposited files: simulation, companion paper, configuration / electrical / mechanical JSON, parts CSV, system schematic, citation, license, and metadata. |
BLADE-CUAS is at TRL 2-3 for hardware (Preliminary Design Phase) and TRL 3-4 for the reference simulation (analytical and experimental proof-of-concept in a browser-native environment). All performance figures on this page are design targets for the reference simulation. Hardware build, empirical sensor calibration, and field measurement are planned future work (as of October 2026).
Reference configuration with parts list (PARTS.csv), electrical and mechanical connection maps (JSON), build guide, and a complete system schematic. No hardware has been fabricated.
Browser-native nine-stage pipeline, six scripted scenarios + free-play demonstrated in simulation, deterministic seeded PRNG, SHA-256 audit chain (FIPS 180-4).
Controlled-impedance carrier PCB design, fabrication, and integration testing across the full 130-component reference node graph.
Hardware-in-the-loop calibration of the five sensor modalities and Dempster-Shafer weight tuning against live track data.
TLA+ specification of the four-tier authority state machine and the evidence-chain invariants, building on the existing AUTHREX TLA+ specifications.
Controlled-range evaluation with a participating federal-SLTT partner, focused on the authority-handoff and evidence-export workflows.
BLADE-CUAS provides open artifacts for independent examination of the governance pipeline behavior, the reference hardware design, and the simulator. All files are published open-access on Zenodo (DOI 10.5281/zenodo.20299604) and mirrored in the repository.
Single self-contained HTML file implementing the full nine-stage pipeline, six scenarios + free-play, deterministic seeded PRNG (xoshiro128**), and a SHA-256 audit hash chain. Re-runs reproduce a configuration-exact decision trace within the declared runtime.
CONFIG / ELECTRICAL / MECHANICAL JSON, PARTS.csv reference BOM, build guide, and the full system schematic (SVG). Interface-defined integration, not vendor-locked.
Six scripted scenarios demonstrated in simulation; no run count or failure rate is asserted. SHA-256 audit chain (FIPS 180-4) with per-input ECDSA P-256 signatures.
RTCA DO-365 (Detect and Avoid MOPS; airspace context, not a counter-UAS standard), MIL-STD-461G / 810G / 1275, FCC Part 15, ASTM F3411 (Remote ID), 14 CFR Part 89, DoDD 3000.09, NIST AI RMF 1.0, and Fed. R. Evid. 901 / 902 / 803(6).
Complete BLADE-CUAS Governance Node reference package. All files are original work by Burak Oktenli (independent researcher). Documents: CC BY 4.0, as recorded on the Zenodo deposit (DOI 10.5281/zenodo.20299604). Code and simulations: MIT License.
The BLADE-CUAS Governance Node is part of the independent authority-governed autonomy research program by Burak Oktenli. It is the sixth domain instantiation of the BLADE governance pipeline, intended to show, at design and simulation level only, that the same architectures specified across defense (BLADE-EDGE), automotive (BLADE-AV), maritime (BLADE-MARITIME), critical infrastructure (BLADE-INFRA), and orbital (BLADE-SPACE) reference designs apply to counter-UAS authority governance under EO 14305 and the FY26 NDAA Safer Skies Act.
Related architectures: SATA · HMAA · CARA · MAIVA · FLAME · ADARA · ERAM
If you reference BLADE-CUAS in scholarly or policy work, please cite as follows.