BLADE-SWARM = Beam-Layer Authority for Directed Engagements, Swarm Node
A reference architecture and a proposed N=10 testbed (reference design, not built) for governing decision authority and audit across an attritable autonomous swarm. In the design and its browser simulation, each agent runs a Byzantine-fault-tolerant two-phase consensus, gated by computed peer trust (SATA), authority tier (HMAA), and weighted multi-agent voting (MAIVA), before the swarm commits to a coordinated action. The architecture is parameterized over N = 10 (proposed testbed baseline, not built), N = 50 (small-scale combined operation), and N = 500 (large-swarm scale, a notional test size chosen for this research). It governs decision authority and audit; it does not govern weapons.
Reference Architecture (TRL 3-4 simulator and formal spec; TRL 2 testbed design) · Eighth BLADE Platform · DOI 10.5281/zenodo.20351198This is NOT a weapon and not a swarm-control autopilot. It is an authority-gating governance layer that sits between the swarm autonomy stack and any coordinated action, computing peer trust, authority tier, and a tamper-evident distributed audit ledger. It is designed to tolerate up to f = (N-1)/3 compromised agents per quorum (the Byzantine bound is an assumption of the specification, not a verified result) and to default to a safe halt under denied or degraded radio-frequency conditions.
BLADE-SWARM is the swarm-scale instantiation of the AUTHREX authority-governance architecture. Where the single-node BLADE platforms govern one autonomous system, BLADE-SWARM governs the collective decision: before a swarm commits to a coordinated action, a quorum of agents must agree, and that agreement must pass the same authority checks that govern a single node. The contribution is a protocol design intended to make this agreement Byzantine-fault-tolerant, authority-bound, and auditable after the fact.
Each agent independently computes peer trust (SATA), evaluates the current authority tier (HMAA), and casts a weighted vote (MAIVA). A two-phase commit then requires an intersecting quorum to agree before the action proceeds. The protocol is designed to tolerate up to f = (N-1)/3 compromised or faulty agents per quorum (an assumption of the specification, not a verified result), to resist Sybil attacks through attested per-node identity, and to halt safely by default when the radio-frequency environment is denied or degraded. Every step writes a signed entry into a hash-chained distributed audit ledger that is gossiped across the mesh, so the swarm's decisions remain reconstructable and tamper-evident.
Attritable autonomy at scale has moved from concept to acquisition priority. Public programs and challenges in this area, such as the Replicator initiative the Pentagon launched in 2023 (moved in late 2025 to the Defense Autonomous Warfare Group, DAWG) and open swarm-autonomy challenges, emphasise large numbers of low-cost autonomous platforms acting in coordination. This research is independent of those programs, and its N = 500 scale is not taken from any of them. As these systems scale, the unsolved problem shifts from flying the swarm to governing it: who, or what, is authorized to commit the collective to an action, on what evidence, and how is that decision proven afterward, especially when communications are contested and some agents may be compromised.
BLADE-SWARM is a fundamental-research contribution toward that authority-governance problem. It treats the swarm as a distributed decision-maker whose commits must be both Byzantine-fault-tolerant and authority-gated, and whose actions must leave a tamper-evident record. The architecture governs decision authority and audit; it does not govern weapons and makes no empirical claims about specific systems, operations, or named officials.
Each agent runs a two-phase consensus protocol gated by three of the seven AUTHREX architectures. The protocol is designed so that no single compromised agent, and no minority faction up to the Byzantine bound, can cause the swarm to commit to an unauthorized action or to escalate its authority tier without an intersecting quorum. This design intent is not asserted as a verified guarantee while the MAIVA CriticalSafe invariant remains open.
Each agent computes a continuous trust score for every peer from attested identity, behavioural consistency, and audit-chain integrity. Low-trust peers are down-weighted in voting and excluded from quorum formation.
Four tiers (T3 autonomous, T2 supervised, T1 confirmed, T0 halt). Tier escalation requires quorum agreement; tier downgrade is asymmetric and can be triggered unilaterally for safety.
Sub-quorum decomposition with Dempster-Shafer weighted voting. A quorum-intersection bound is the design basis for safety when no more than f = (N-1)/3 agents per quorum are compromised; verification is open, so this is not a guarantee.
FLAME contracts the deliberation window under threat density and expands it under ambiguity; CARA provides bounded-liveness recovery and isolates misbehaving agents with a corrective audit entry.
The same protocol and simulator are parameterized over three operating scales. The N=10 baseline is a proposed testbed (reference design, not built); the simulator covers all three scales, including the combined-operation and large-swarm scales.
BLADE-SWARM instantiates the AUTHREX governance pipeline at swarm scale. The pipeline runs once per proposed coordinated action; the consensus and authority stages require an intersecting quorum before the action is allowed to commit.
The protocol is specified in TLA+ (AUTHREX_SWARM.tla), refining the existing AUTHREX_MAIVA module with sub-quorum decomposition, Byzantine fault bounds, FLAME deliberation-window contraction, tier-downgrade asymmetry, and CARA bounded liveness. The specification states 5 safety and 3 liveness properties; model-checking output has not yet been published (the verification report's TLC figures are illustrative), and S5, the Byzantine bound, is an assumption, not a result.
Tier ceiling, no-unauthorized-commit, quorum intersection, audit-chain integrity, and the Byzantine bound (S1 through S5), as stated in the specification. No model-checking output for them has been published; S5, the Byzantine bound, is a precondition of the model (an assumption), not a result.
Eventual commit-or-abort, eventual tier restoration, and CARA termination (L1 through L3), stated so that the protocol is required to make progress and recover under fault; no model-checking output for them has been published.
No model-checking result is claimed until a dated TLC configuration file and log are published; even then, a check of a reduced-scale instance would not be a proof for arbitrary N. The specification and the verification report (which lists the intended TLC configuration and gives illustrative TLC figures) are included in the repository and the Zenodo deposit; no TLC configuration file or log is included.
BLADE-SWARM is framed against the public policy and standards instruments that govern autonomous systems and AI risk. These are cited as context that the architecture is designed to support; no empirical claims are made about specific programs or officials.
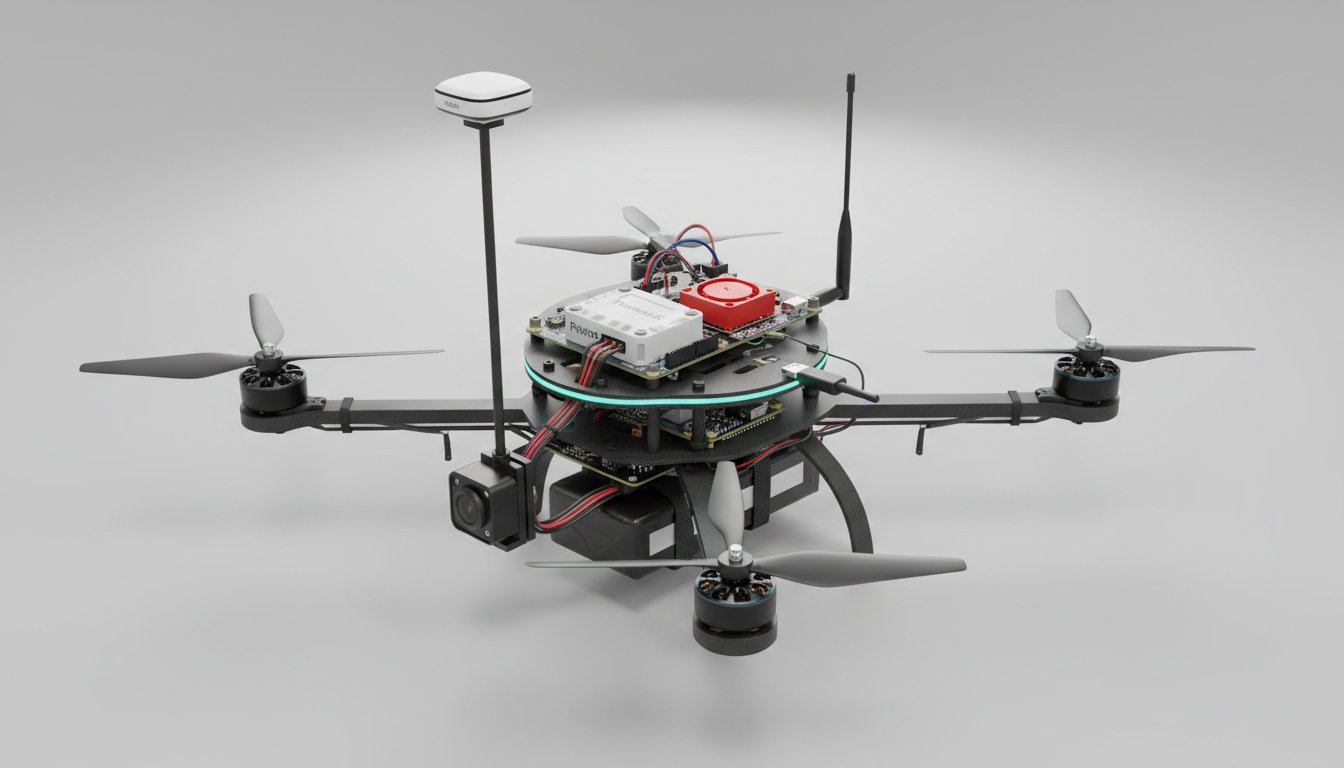
The reference node is a Holybro X500 V2 quadrotor with a COTS governance stack. One node is approximately $1,333; the proposed N=10 testbed baseline (not built) would be approximately $13.3K. The full parts list, electrical and mechanical connection maps, and assembly guide are in the repository.
| Subsystem | Component | Cost |
|---|---|---|
| Frame + propulsion | Holybro X500 V2 kit (motors, ESCs, props, PDB) | ~$400 |
| Flight controller | Pixhawk 6X autopilot | ~$300 |
| Companion compute | Raspberry Pi 5 8GB + active cooler | ~$120 |
| Mesh radio | LoRa SX1276 (915 MHz) + Wi-Fi 6 USB | ~$55 |
| Navigation | Holybro M9N GNSS + magnetometer | ~$60 |
| Root of trust | Microchip ATECC608B secure element | ~$15 |
| Power | 4S 5000 mAh LiPo + monitor | ~$80 |
| Indicator + mounting | Addressable LED ring, dampers, hardware, masts | ~$53 |
| Per-node total | approx. (optional camera +$50) | ~$1,333 |
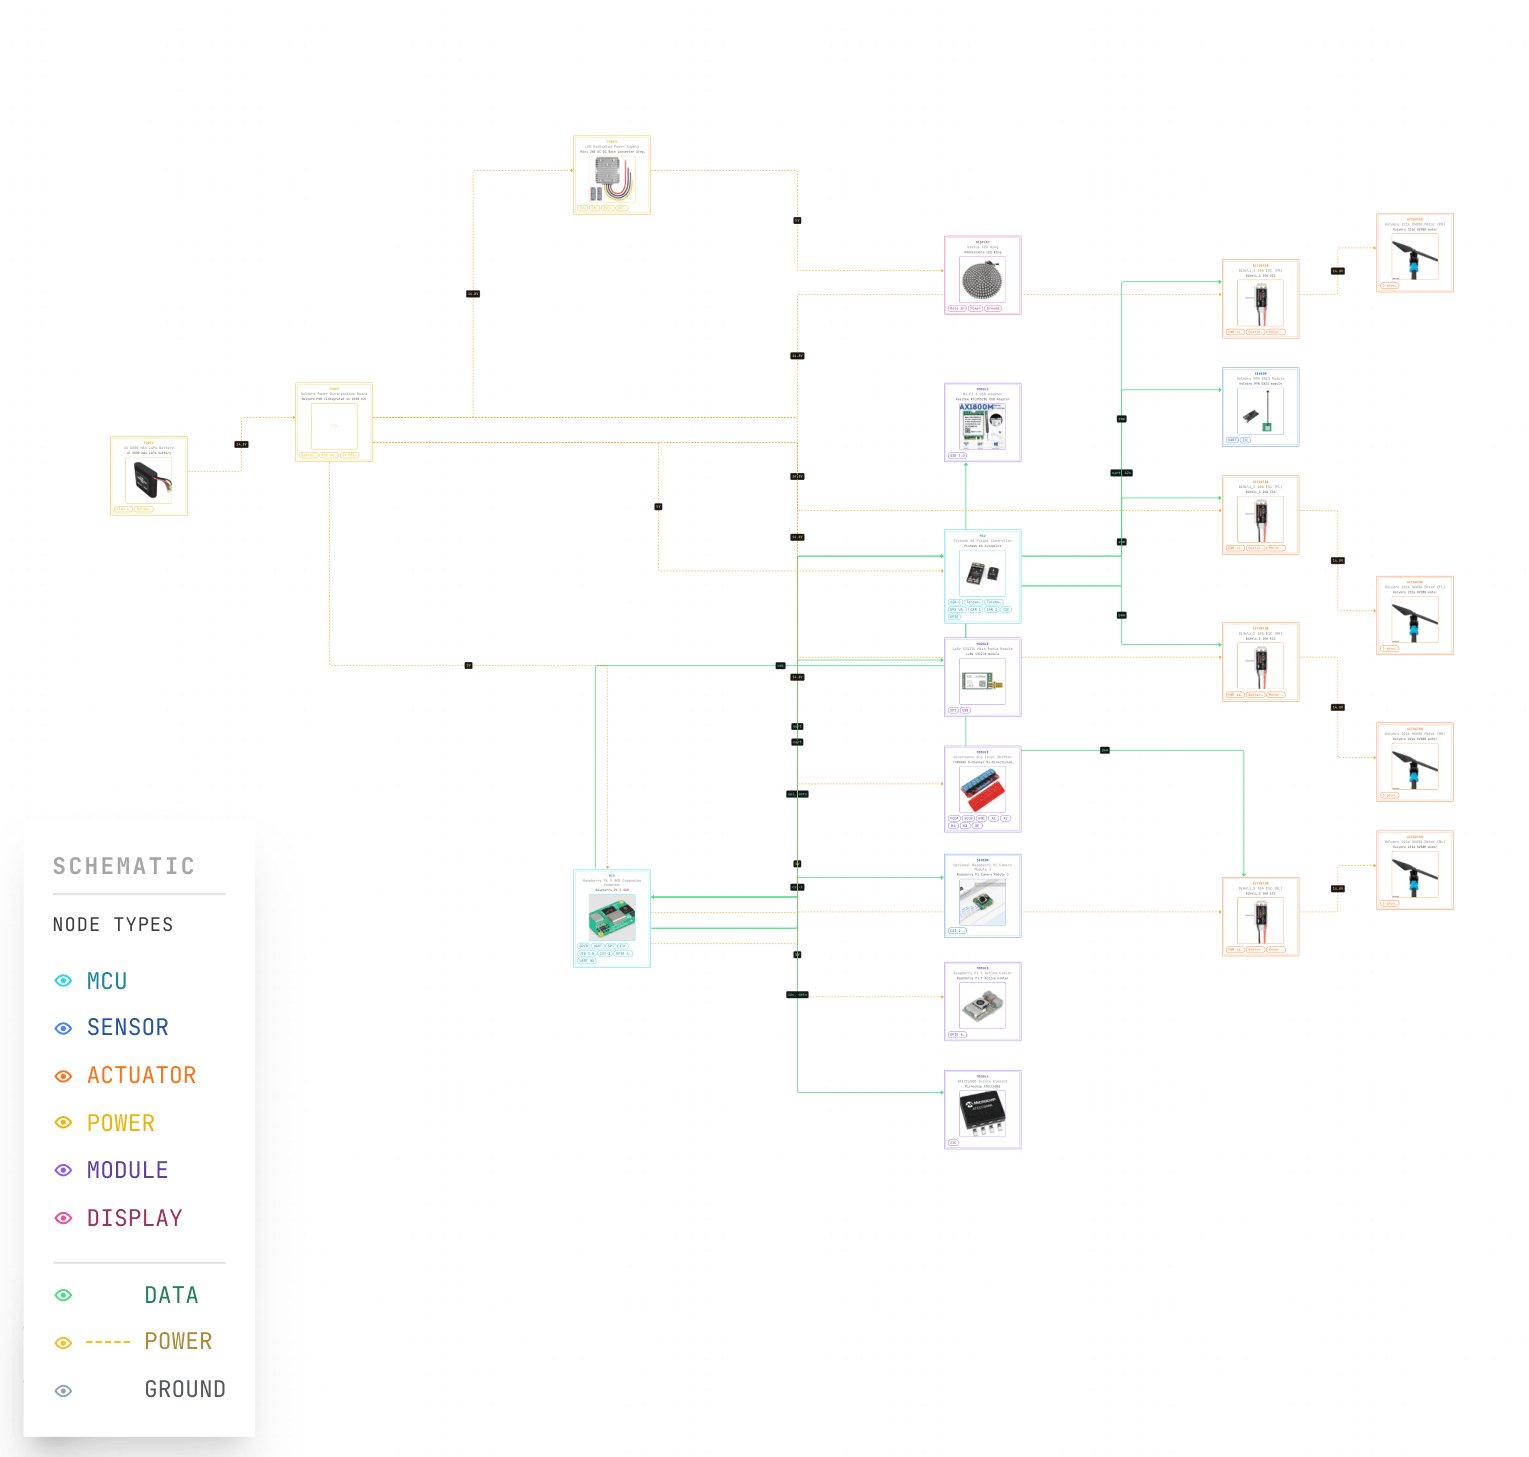
The node electrical design, power rails, data interfaces, and the governance-bus level shifter that bridges the Pixhawk 6X, the Raspberry Pi 5, and the ATECC608B secure element. The full-resolution schematic is available as a download.
A single-file, deterministic discrete-event simulator runs the full consensus and authority protocol in the browser, parameterized over N = 10, 50, and 500, with five scripted scenarios from nominal operation through denied and degraded conditions. It visualises the live pipeline, the per-node tier state, and the growing distributed audit ledger.
Launch Swarm SimulatorBLADE-SWARM is the eighth platform in the BLADE family, each instantiating the AUTHREX authority pipeline in a different domain. It develops the swarm-governance direction first set out in the single-agent Authority-Governed UAV Platform (HMAA-UAV) program, carrying the shared SATA-HMAA-CARA governance lineage from a single governed drone design (build in progress) to coordinated swarms of N = 10 to N = 500 agents in design and simulation; the two platforms are intended to complement each other, HMAA-UAV as the single-agent foundation and BLADE-SWARM as the multi-agent extension.
Single-agent foundation: Authority-Governed UAV Platform (HMAA-UAV) · Authority-Governed Rover Testbed
If you reference BLADE-SWARM in scholarly or policy work, please cite as follows.