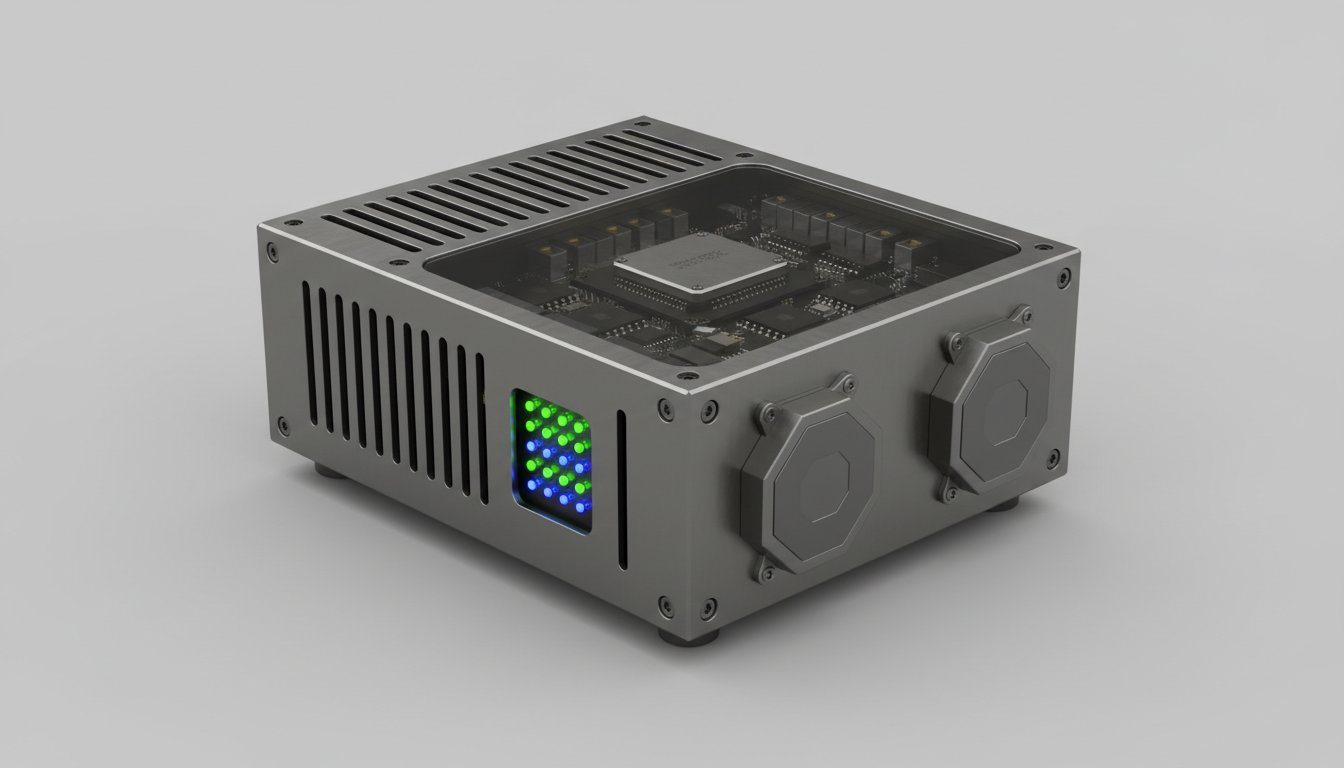
BLADE-AGENT-HSM = Beam-Layer Authority for Directed Engagements, Agent Hardware Security Module · the hardware companion to the AUTHREX-AGENT software shim
A reference design (design package and bill of materials; not built) for a tamper-evident hardware root of trust for autonomous AI agents. As designed, BLADE-AGENT-HSM would sign an agent's audit ledger with non-exportable ECDSA keys held in a secure element (Common Criteria EAL6+ design target), store the authority-tier state in a TPM 2.0 PCR bank, derive per-tool authorization tokens, aggregate sub-agent spawn-quorum signatures, and trigger a key-zeroizing abort on physical tamper. It is designed to attach to a host as a USB-A stick or an M.2 Key-E module.
Reference Design (not built; TRL 2-3 silicon / 3-4 emulator) · Seventh BLADE Platform · DOI 10.5281/zenodo.20299821 · v4.0BLADE-AGENT-HSM is the hardware half of a two-piece program: the AUTHREX-AGENT software shim runs the authority lifecycle, and this module is designed to make that lifecycle non-forgeable by moving the signing keys, the tier state, and the audit ledger into tamper-evident silicon. Together they are designed as a response to the CISA, NSA AI Security Center, and Five Eyes joint guidance Careful Adoption of Agentic AI Services (1 May 2026), FY26 NDAA Sections 1513 and 6601, and NIST SP 800-53 Rev. 5.
The rapid 2026 adoption of autonomous, tool-using AI agents created a security gap that, this work argues, software alone cannot close: when an agent can spend, call tools, and spawn sub-agents on its own, its authority and its record of decisions are only as trustworthy as the software holding them, and that software is exactly what an indirect prompt injection or a compromised host can subvert. The mission of this work is to specify a tamper-evident hardware root of trust that makes an agent's authority tier and audit ledger non-forgeable, so that an agent cannot exceed its granted authority or rewrite its history without breaking the device, and breaking the device leaves evidence.
Agent permissions today live in software the agent process can read and, under compromise, alter. The logs that should prove what an agent did are written by the same stack being audited. In the standards and literature reviewed for this work, no portable hardware was identified that holds the authority tier itself, signs each action with a non-exportable key, and refuses to operate after a physical tamper.
General-purpose secure elements and TPMs exist, but none identified in the standards and literature reviewed for this work binds the specific authority lifecycle of an AI agent (graded tiers, per-tool tokens, spawn-quorum aggregation, deterministic tamper response) to a tamper-evident device that an agent or its host can attach over USB or M.2.
BLADE-AGENT-HSM extends the AUTHREX governance framework (specified across the BLADE reference designs and demonstrated in their browser simulations) into the agentic-AI domain as the seventh BLADE platform and the first hardware root of trust in the family. It is the hardware companion to the AUTHREX-AGENT software shim, contributing a non-exportable-key signing path, TPM-resident tier state, HKDF-derived per-tool tokens, spawn-quorum aggregation, and a deterministic multi-modal tamper cascade, all modeled in an adversarial high-assurance emulator that passes 275 deterministic checks.
Assurance boundary. This is a research demonstrator. Hardware maturity is approximately TRL 2-3 (specification and reference design); the emulator is approximately TRL 3-4. The emulator runs real Web Crypto primitives, but no hardware has been built and no FIPS, Common Criteria, EAL, NSA, NASA, or DoD endorsement, validation, or certification of any kind is claimed. Silicon timing is modeled, not measured; post-quantum fields model interface shape only.
In 2026 the United States and its closest partners moved from encouraging agentic AI to governing it. On 1 May 2026 the Cybersecurity and Infrastructure Security Agency, the NSA AI Security Center, and the Five Eyes cyber agencies issued joint guidance, Careful Adoption of Agentic AI Services, calling for cryptographically verified agent identity, logging of every agent action, and least-privilege permissions for autonomous agents. The FY2026 National Defense Authorization Act addressed related AI security requirements in Sections 1513 and 6601.
This work argues that software controls alone cannot satisfy that guidance, because the software is the attack surface. A hardware root of trust changes the trust assumption: when the signing keys live in a secure element (EAL6+ design target), the authority tier lives in a TPM, and every action is signed by hardware, the design is intended so that an attacker cannot escalate an agent past its tier or forge its audit trail without physically defeating the device, and so that the device records the attempt. This is the principle that secures payment and identity hardware, applied to the authority of autonomous AI.
BLADE-AGENT-HSM, paired with the AUTHREX-AGENT software shim, is a research contribution toward closing that gap. It makes no empirical claims about specific products or incidents, claims no government endorsement, and is a reference design at research-demonstrator maturity.
The market has mature secure elements, TPMs, and a growing set of software frameworks for agent identity and tool permissions. None identified in the standards and literature reviewed for this work binds the AI-agent authority lifecycle to a tamper-evident device the agent can carry.
BLADE-AGENT-HSM is designed to address all four as an attachable module that would integrate over USB-A or M.2 Key-E. It would not run the agent's model; it is designed to anchor the agent's authority and the record of it in hardware.
BLADE-AGENT-HSM is deliberately one half of a program. The AUTHREX-AGENT software shim, available as a prototype, implements the authority lifecycle (tiering, deliberation, recovery, ledger) in software; BLADE-AGENT-HSM is then designed to close the production-readiness gap by making the keys non-exportable, the tier hardware-attested, and the ledger tamper-evident. The same root-of-trust design is already specified in the BLADE-EDGE, BLADE-AV, and BLADE-INFRA reference designs; this reference design extracts it into a standalone, attachable device design.
The authority-lifecycle shim. Runs the T3 to T0 tiering, the deliberation window, recovery, and an ECDSA P-256 audit ledger in software. Available as a prototype; software trust assumptions. TRL 3-4.
The hardware root of trust (reference design; not built). Non-exportable keys in a secure element (EAL6+ design target), tier state in a TPM 2.0, tamper-evident audit ledger. USB-A stick or M.2 Key-E. ~$199 per unit. TRL 2-3 silicon.
Together they are designed to address the cryptographically verified agent identity, action-logging and least-privilege expectations of the CISA, NSA, and Five Eyes agentic-AI guidance (self-assessed; not an official determination).
BLADE-AGENT-HSM is not designed to run an AI model. As specified, it exposes a fixed 64-byte command frame (over USB-HID for the stick, or SPI-slave for the M.2 module) with exactly five authority-bearing operations. The host or the AUTHREX-AGENT shim calls these; the keys and the tier state stay inside the device.
| PCR | Holds | Extended |
|---|---|---|
| PCR0 | Authority tier state (T3 / T2 / T1 / T0) | On every tier transition |
| PCR1 | Audit ledger chain | On every audit_sign |
| PCR2 | Tool policy | Sealed at provisioning |
| PCR3 | Spawn quorum | On every spawn event |
| PCR4 | Tamper cause code | Only on tamper |
| PCR5-PCR7 | Reserved for integrator policy | Integrator-defined |
The frame carries a 4-byte opcode, a 2-byte length, a payload up to 26 bytes, and a 32-byte HMAC-SHA-256. The full layout is in the Interface Control Document (ICD-AGENT-HSM-001).
As designed, BLADE-AGENT-HSM holds the four-tier HMAA authority state in the TPM and surfaces it on a tri-colour indicator LED, so the authority state of an agent is visible physically and is not something the agent process can misrepresent.
| Tier | Indicator | Description |
|---|---|---|
| T3 | Green | Autonomous. The agent may act within its tool policy without per-action confirmation. Every action is still signed and extended into the ledger. |
| T2 | Amber | Supervised. High-consequence actions are signed only after a supervising party acknowledges. Non-acknowledgment defaults to refusal. |
| T1 | Red | Confirmed. The most consequential actions require an explicit operator confirmation recorded with full context. |
| T0 | Blinking red + alarm | Halted and locked. Entered on tamper, attestation failure, or operator halt. Keys are zeroized; the ABI refuses every opcode except pcr_quote until re-provisioning. |
Provisioning state. During the provisioning ceremony the tier LED shows a slow blue pulse; a green power LED is solid whenever the 3.3V rail is stable. Each agent carries a sealed tool policy (PCR2) that defines its tier ceiling.
As designed, BLADE-AGENT-HSM is a sealed module on a four-layer board whose inner layers carry an active tamper mesh. Several independent sensing paths feed the deterministic tamper cascade.
| Sensing Path | Mechanism | Trips On |
|---|---|---|
| Active PCB mesh | Continuous low-current serpentine loop on layers L2/L3 (8-12 ohm), polled every 10 ms | Short, open, or impedance shift over 5 percent |
| Voltage-glitch detector | Windowed comparator on the 3.3V rail | Undervoltage below 2.7V or overvoltage above 3.6V |
| Thermal monitor | High-accuracy I2C temperature sensor with alert to the MCU | Out-of-envelope temperature (thermal-tamper) |
| Supply supervisor | Windowed reset supervisor on the 3.3V rail | Rail excursions trigger an MCU reset |
A physical tamper-evident seam label spans the enclosure and tears on opening, with its serial recorded against the device serial number. The specified response is deterministic: a tampered device stops signing until an authorized re-provisioning ceremony.
Every authority-bearing action is signed and recorded so the agent's history is verifiable after the fact.
As designed, each audit entry is signed with an ECDSA P-256 key resident in the secure element (EAL6+ design target), whose extractable attribute is fixed false at provisioning. The private key is designed never to leave the device, so that a signature would tie each record to a specific physical device identity.
Each entry references the previous entry's hash, forming an append-only chain that is also extended into TPM PCR1. A periodic TPM quote over the PCR selection provides an attested checkpoint that can be exported and anchored externally.
The reproducibility package includes a deterministic golden trace and a P-384 signed anchor over the event count, the final PCR digests, and the trace SHA-256. The bundled verifier re-derives the PCR chain, checks the ECDSA signature on every entry, and validates the anchor; truncation or substitution fails verification.
Trust-root caveat. The audit anchor's attestation public key travels inside the evidence file, so it is not a trust root on its own. Adversarial forgery resistance requires the verifying party to pin the device's attestation identity out-of-band. Absent that pin, the verifier honestly reports integrity-and-same-session trust only.
The BLADE-AGENT-HSM design uses a three-layer security architecture anchored in hardware. Because the device is the root of trust, the model protects the keys, the identity, and the integrity of the evidence chain.
NXP EdgeLock SE051 (CC EAL6+ design target) is specified to hold non-exportable ECDSA P-256/P-384 keys, plus ECDH, AES-256-GCM, SHA-256/384, and HKDF. Infineon SLB 9670 TPM 2.0 (FIPS 140-2 Level 2 design target) owns the PCR bank, sealed storage, quote, and attestation key. A discrete ATSHA204A adds second-source entropy and a device serial.
An STM32L432 Cortex-M4F MCU is specified to run the ABI dispatcher and the authority logic as deterministic firmware isolated from the host. It is designed to refuse any action above the active tier, gate all signing on the tamper state, and serve only pcr_quote after a tamper latch.
Active mesh, voltage-glitch, and thermal sensing are designed to drive a zeroize-and-lock cascade. A USB ESD device guards the host interface. Every action is ECDSA-signed and hash-chained into PCR1, with a P-384 signed golden-trace anchor for external verification.
In the reference design, a single 30 mm by 80 mm four-layer PCB supports two enclosures: a USB-A stick (84 by 24 by 9 mm, two-piece clamshell with a tamper-evident seam label) for development, red-team rehearsal, and forensic verification; and an M.2 Key-E module (Type 2280) for production edge and rack deployment, where the host chassis provides physical security. The USB-A variant regulates host 5V to 3.3V on board; the M.2 variant takes 3.3V from the host directly.
| Reference | Component | Role |
|---|---|---|
| U1 Secure Element | NXP EdgeLock SE051C2HQ1/Z01V (CC EAL6+ design target) | Non-exportable ECDSA P-256/P-384 keys; ECDH, AES-256-GCM, SHA-256/384, HKDF, on-chip RNG. I2C. |
| U2 TPM | Infineon SLB 9670VQ2.0 TPM 2.0 (FIPS 140-2 L2 design target) | PCR bank (PCR0-7), quote, sealed storage, attestation key. SPI. |
| U3 Governance MCU | STMicro STM32L432KCU6 (Cortex-M4F, 80 MHz) | USB-FS device; USB-HID stack, I2C/SPI master, tamper polling, ABI dispatch. |
| U4 Tamper Sensor Block | Active mesh + voltage-glitch + thermal (I2C temperature sensor) | Multi-modal physical intrusion detection feeding the tamper cascade. |
| U5 TRNG / Serial | Microchip ATSHA204A | Second-source entropy for the secure element and a unique device serial number. |
| U6 / U7 Power | TI TPS73633 LDO (5V to 3.3V) + TPD2E001 USB ESD + MAX16162 supervisor | Clean 3.3V rail, host-interface ESD protection, and undervoltage/overvoltage supervision. |
| U8 / U9 Timing | Abracon ABS06 RTC crystal + ABM3B HSE crystal | Real-time clock for ledger timestamps and the MCU high-speed clock. |
| Indication | Green power LED, tri-colour tier LED, red alarm LED, Kingstate KPT-G2810 piezo | Surfaces the active authority tier, provisioning state, and tamper alarm. |
| J1 / J2 Host Interface | USB-A castellated pads + M.2 Key-E gold fingers (75-position) | Two attachment options; not co-populated on a given unit. |
Four-layer FR-4, 1.6 mm, ENIG finish; inner layers L2/L3 carry the active tamper mesh. Full bill of materials, pin-level interconnect, and connection maps are in the Zenodo deposit (DOI 10.5281/zenodo.20299821).
Unlike the BLADE domain node designs, which specify gating of a physical effector, the BLADE-AGENT-HSM design has no actuator that acts on the outside world. Its only outputs are a signed authorization, a PCR extension, a ledger entry, an indicator state, and a tamper alarm. It is designed to enforce authority by withholding a signature: an action the agent cannot get signed is an action it cannot prove was authorized, and a tier-bound tool token the device will not derive is a tool the agent cannot use.
Why this matters. The device is designed so that it cannot move money, call a tool, or send a command on its own. It is a checkpoint, not an actor. This keeps the intended safety property simple: within the design's threat model, the worst a compromised host can do is be refused a signature or a token, and a detected physical attack is designed to zeroize the keys and leave a recorded tamper event. It is the inverse of the effector interlock (SIL 3 design target) specified in the physical-domain BLADE reference designs, the same root-of-trust idea applied to a device that authorizes rather than acts.
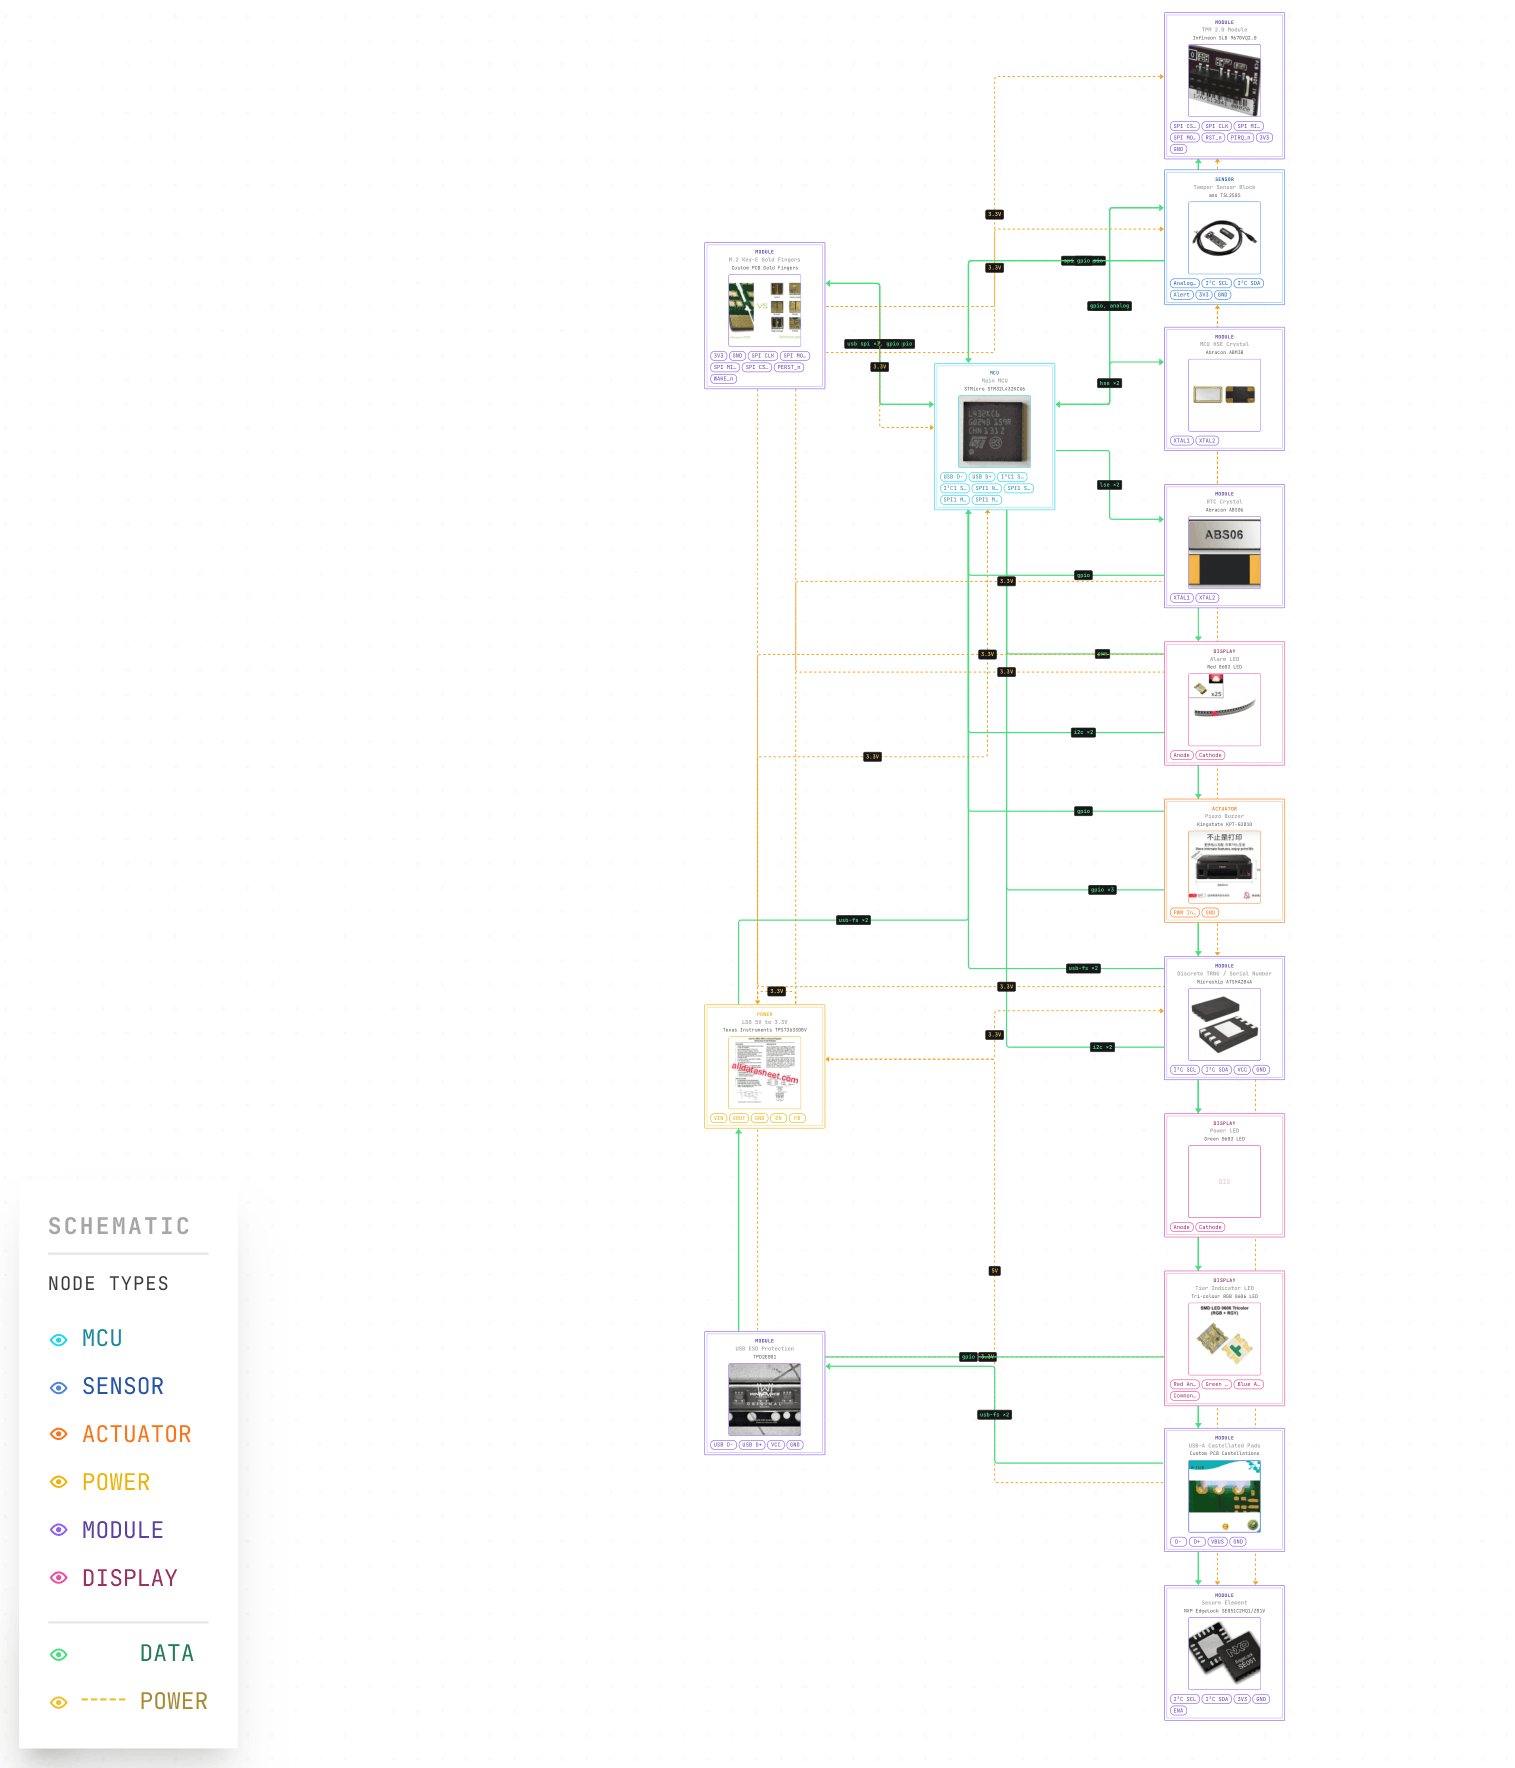
Full subsystem node graph color-coded by type (MCU, Sensor, Actuator, Power, Module, Display). Shows the STM32L432 governance MCU at the center, the TPM 2.0, secure element, and discrete TRNG cryptographic subsystems, the tamper sensor block, the tier-indicator, alarm, and power LEDs, the piezo buzzer, the LDO power regulation and USB ESD protection, the RTC and HSE crystals, and the USB-A and M.2 Key-E host interfaces with data and power links.
BLADE-AGENT-HSM is specified as a low-cost secure module, an order of magnitude cheaper than the domain governance node designs. The reference bill of materials is dominated by the three cryptographic devices. The figures below are from the reference BOM and the first-article engineering estimate in the deposit.
| Item | Reference Cost |
|---|---|
| Secure element (SE051, EAL6+ design target) | $35.00 |
| TPM 2.0 (SLB 9670) | $25.00 |
| Governance MCU (STM32L432) | $18.00 |
| Tamper sensor block + TRNG + supervisor | ~$32.00 |
| Power, ESD, crystals, indicators, passives | ~$5.00 |
| PCB (4-layer, ENIG) + enclosure + assembly | ~$84.00 |
| Per-unit total (qty 10-100) | ~$199 |
| Non-recurring engineering (first article) | ~$8,250 |
| First-article total | ~$8,449 |
Non-recurring engineering covers PCB layout, firmware, debug tooling, test fixtures, and documentation. At volume the per-unit cost falls further; the cryptographic devices set the floor.
| Parameter | Value |
|---|---|
| Form factor | USB-A stick (84 x 24 x 9 mm) or M.2 Key-E module (Type 2280), single 30 x 80 mm 4-layer PCB |
| Power | Host 5V (4.75-5.25V) → 3.3V rail (±3%); 80 mA typical, 250 mA peak during ECDSA P-384 signing |
| Operating temperature | -10 C to +75 C |
| Host interface | USB full-speed HID (stick) or SPI-slave (M.2); 64-byte fixed ABI frame, 5 opcodes |
| Secure element | NXP EdgeLock SE051 (CC EAL6+) · non-exportable ECDSA P-256/P-384, ECDH, AES-256-GCM, SHA-256/384, HKDF |
| TPM | Infineon SLB 9670 TPM 2.0 (FIPS 140-2 Level 2) · PCR0-7, quote, sealed storage |
| Governance MCU | STMicro STM32L432KCU6 (Arm Cortex-M4F, 80 MHz) |
| Tamper detection | Active PCB mesh (L2/L3, 8-12 ohm, polled 10 ms) + voltage-glitch window (2.7/3.6V) + thermal monitor → zeroize and T0 lock |
| Authority model | Four-tier (T3 green / T2 amber / T1 red / T0 blink + alarm), TPM-resident in PCR0 |
| Evidence chain | ECDSA P-256 signed, hash-chained, PCR1-bound; P-384 signed golden-trace anchor |
| Standards alignment (self-assessed) | CISA / NSA / Five Eyes agentic-AI guidance · FY26 NDAA §1513 and §6601 · NIST SP 800-53 Rev. 5 · FIPS 140-2 / 140-3 · TPM 2.0 (TCG) |
| Reference cost | ~$199 per unit (qty 10-100); ~$8,250 NRE; ~$8,449 first article |
| Maturity | TRL 2-3 silicon · TRL 3-4 emulator |
The BLADE-AGENT-HSM emulator models the specified hardware behavior in the browser with real Web Crypto primitives (ECDSA P-256/P-384, SHA-256, HKDF) and no backend. It models the PCR measurement chains, the audit-ledger signing, the tier transitions, the spawn quorum, the per-tool zero-trust tokens, and the failure-mode scenarios, including a voltage glitch, an electronic-warfare hazard with recovery, split-brain ledger reconciliation, and Byzantine fault isolation. It exports a signed evidence bundle and runs a browser self-test.
The emulator and its core are checked by a bundled test suite of 275 deterministic checks across seven batteries (275 of 275 passing, confirmed over three reruns), plus a software-only-versus-HSM baseline that estimates, in emulation, what the hardware anchor would add. A deterministic golden trace and a P-384 signed anchor allow independent verification.
The seven batteries cover standalone logic, adversarial cases, the embedded-in-HTML core, red-team logic, and trust-root pinning. Critical findings closed include real signature verification on every audit entry (not a line count), enforced fault knobs, true tamper-origin-tier capture, and a P-384 anchor that fails on truncation. With an out-of-band identity pin, the verifier resists adversarial trace forgery, including anchor re-key attacks. These are emulator and reference-design results; no hardware has been built.
BLADE-AGENT-HSM is the seventh instantiation of the AUTHREX authority-governance framework and the first dedicated hardware root of trust in the family. The six domain governance node designs each specify a trust anchor internally; the BLADE-AGENT-HSM reference design extracts that anchor into a standalone, attachable device design and pairs it with the AUTHREX-AGENT software shim, so that the same hardware-rooted authority and audit chain would be available to software AI agents and to any BLADE node. The seven governance architectures (SATA, HMAA, ADARA, MAIVA, FLAME, CARA, ERAM) are reused in their HSM-specific roles: attestation, tier enforcement, and deterministic recovery anchored in silicon.
Related platforms: Rover Testbed (~$484) · UAV Platform (~$4,200) · BLADE-EDGE (defense, ~$139K) · BLADE-AV (automotive, ~$16K) · BLADE-MARITIME (maritime, ~$43K) · BLADE-INFRA (infrastructure, ~$12K) · BLADE-SPACE (orbital, ~$505K) · BLADE-CUAS (counter-UAS, ~$43.5K) · BLADE-AGENT-HSM (agentic AI, ~$199) · BLADE-SWARM (swarm autonomy, ~$1,333/node) · BLADE-INFRA-OT (IT/OT bridge governance, 1U fanless) · BLADE-FINANCE (financial-sector governance, ~$9K). Twelve hardware platforms: two physical research testbeds whose build is in progress (the rover and the UAV) and ten domain reference designs that have not been built; governance-stack portability is shown at design and simulation level only.
No SDK package has been published; the code below illustrates a proposed interface. In the proposed interface, the AUTHREX-AGENT shim would call BLADE-AGENT-HSM through the same unified API proposed across the BLADE family: an agent would open the device, request an authorization or a tool token, and receive a hardware-signed result, with only the configuration changing between domains.
Cross-domain portability: the same proposed API would serve BLADE-AGENT-HSM and the six BLADE domain reference designs. Switching from a defense node to an AI agent would change the configuration, not the application code.
The BLADE-AGENT-HSM companion paper (16 sections, 5 figures, 28 references), the Interface Control Document, the host-integration guide, and the complete reference-design files are deposited on Zenodo under DOI 10.5281/zenodo.20299821 (CC BY 4.0, v4.0).
| Document | Description |
|---|---|
| Companion Paper (PDF) | A Reference Hardware-Root-of-Trust Design and Verified Emulator for Agentic-AI Authority Governance. |
| Interface Control Document | ICD-AGENT-HSM-001: full ABI frame layout, pinout, and PCR allocation. |
| Integration Guide | Host-integration guide for the USB-A and M.2 variants. |
| Full Repository | All deposited files: emulator, paper, ICD, hardware reference files, and test artifacts. |
BLADE-AGENT-HSM hardware is at approximately TRL 2-3 (specification and reference design); the emulator is at approximately TRL 3-4 (a research demonstrator running real Web Crypto). All silicon performance figures are design targets; silicon timing is modeled, not measured. Board fabrication, the provisioning key ceremony, and tamper-mesh calibration are planned future work (as of October 2026).
Reference design with the system schematic, four-layer stack-up, full BOM, pin-level interconnect, and both enclosure variants. No hardware has been built; no hardware coupon is included.
Browser-native, real Web Crypto, deterministic. 275 of 275 checks across seven batteries, a software-only-versus-HSM baseline, and a P-384 signed golden trace.
Build the USB-A and M.2 Key-E first articles, bring up the secure element, TPM, and host interface, and verify the ABI against the golden vectors.
Define and test the on-device key-generation ceremony, the out-of-band identity pin, and the baseline PCR quote export.
Calibrate the active-mesh impedance threshold and the voltage and thermal windows, and verify the deterministic zeroize-and-lock cascade on physical intrusion.
Move the ML-DSA fields from interface model to a real hybrid signature path, extending the CNSA 2.0 hybrid-signature work modeled in the emulator.
BLADE-AGENT-HSM provides open artifacts for independent examination of the authority behavior, the reference hardware design, and the emulator. All files are published open-access on Zenodo (DOI 10.5281/zenodo.20299821) and mirrored in the repository.
A self-contained HTML emulator with real Web Crypto, deterministic clock, failure-mode scenarios, evidence-bundle export, and an in-browser self-test.
System schematic, four-layer stack-up, full BOM (27 line items), electrical and mechanical connection maps, and the host-integration guide and ICD.
Seven Node test batteries (275 deterministic checks), a software-only-versus-HSM baseline, a deterministic golden trace, and a P-384 signed anchor, with a machine-readable test report.
CISA / NSA / Five Eyes agentic-AI guidance, FY26 NDAA Sections 1513 and 6601, NIST SP 800-53 Rev. 5, FIPS 140-2 / 140-3, and the TCG TPM 2.0 specification.
BLADE-AGENT-HSM reference package. All files are original work by Burak Oktenli. The deposit is published under CC BY 4.0 on Zenodo (DOI 10.5281/zenodo.20299821), as recorded there; the emulator and other code on this site are also offered under the MIT License.
The BLADE-AGENT-HSM Hardware Root of Trust is part of the independent authority-governed autonomy research program by Burak Oktenli. It is the seventh domain instantiation of the BLADE governance framework and the first hardware root of trust in the family, intended to show, at design and emulator level only, that the same authority and evidence design developed across defense (BLADE-EDGE), automotive (BLADE-AV), maritime (BLADE-MARITIME), critical infrastructure (BLADE-INFRA), orbital (BLADE-SPACE), and counter-UAS (BLADE-CUAS) reference designs applies to securing autonomous AI agents.
Related architectures: SATA · HMAA · CARA · MAIVA · FLAME · ADARA · ERAM
If you reference BLADE-AGENT-HSM in scholarly or policy work, please cite as follows.